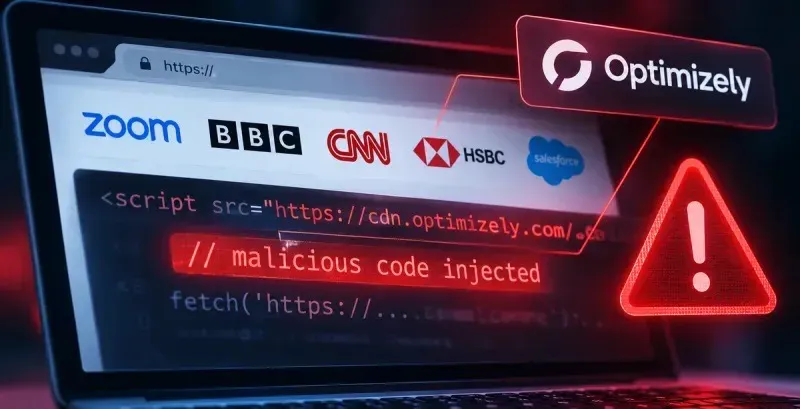
Visitors to at least 178 well-known websites were exposed to malware on 16 November that could secretly swap cryptocurrency wallet addresses and steal credit card details, security researchers have confirmed. The attack has been named Optimjack.
The affected sites belong to organisations such as Zoom, the BBC, CNN, Salesforce, GitLab, IKEA, HSBC, Equifax, Air France-KLM, Ledger and Peacock. The malware was delivered through Optimizely, a widely used service that many companies rely on for website testing and personalisation.
According to Scott Helme of Report URI, who first documented the campaign, the malicious code ran for most of the day on Monday. It was designed to replace legitimate crypto wallet addresses with ones controlled by the attackers whenever a user copied an address on an affected page. It could also capture credit card numbers entered into forms on those sites. The code also attempted to target older iPhones and iPads.
Researchers traced roughly $6,600–$7,000 in cryptocurrency that reached wallets linked to the attackers during the incident. The full extent of any credit card or other data theft is not yet known. Most of the malicious code was removed by Monday evening after the problem was identified.
Optimizely later confirmed that an attacker had exploited a vulnerability in its platform’s account signup process to plant the code. The company said it has fixed the issue, removed the injected scripts, secured affected accounts and notified customers.
Security experts advise anyone who visited major websites on 16 November and copied a cryptocurrency address or entered card details to double-check recent transactions and monitor bank statements. Crypto users are reminded to always verify wallet addresses carefully before sending funds, rather than relying only on copy-and-paste. Investigations into the full scope of the attack and the people behind it are continuing.